
Custom Development
Alcohol Delivery Market Share and Trends: Size, Growth, & Business Opportunities
7 Apr 2026
Virtual care is convenient—but is it secure? With telehealth on the rise, protecting patient data is more critical than ever. A HIPAA-compliant telehealth platform ensures that sensitive health information stays safe while care happens online.
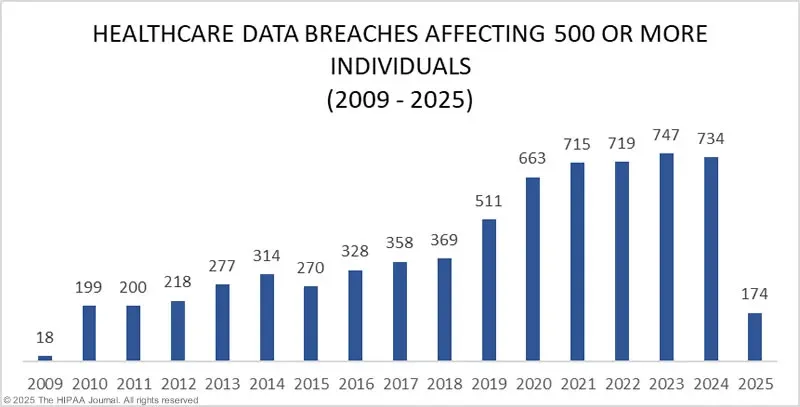
By the end of 2024, hacking and IT incidents were responsible for 276.8 million breached healthcare records, a 64 % increase from 2023, with 14 separate breaches exposing over 1 million records each. (Source: HIPAA Journal)
So, how can telehealth platforms protect patient privacy while keeping care smooth and simple?
This is where HIPAA rules step in. When done right, it secures sensitive information, helps you meet legal standards, and gives patients the peace of mind they deserve. Whether you’re a healthcare provider, admin, or someone deciding which telehealth tool to use, knowing what makes a platform HIPAA-compliant is essential.
In this guide, we’ll break it down. You’ll learn what to look for in a HIPAA-compliant telehealth platform, how it works behind the scenes, and how it helps you focus on what matters most: delivering great care without worrying about data security.
Telehealth has unlocked a new level of access in healthcare. But this convenience comes with a tradeoff—every virtual consultation, message, and digital health record opens a new doorway to potential data exposure.
Healthcare data is one of the most valuable targets for cybercriminals.
According to the U.S. Department of Health and Human Services, healthcare data breaches have doubled in the last five years. That’s not just bad PR—it’s lawsuits, lost trust, and regulatory fines.
A HIPAA-compliant telehealth platform is the guardrail that ensures virtual care doesn’t compromise patient privacy or institutional credibility.
HIPAA rules set the baseline for your digital healthcare services. It's what separates platforms that last from those that fail under scrutiny.
Before exploring specific telehealth requirements, it's important to understand what HIPAA-compliant telehealth platform fundamentally means for virtual care delivery and who bears responsibility for maintaining these standards.
The Health Insurance Portability and Accountability Act (HIPAA) establishes national standards to protect sensitive patient health information.
For telehealth specifically, compliance centers on safeguarding Protected Health Information (PHI) and electronic Protected Health Information (ePHI) during virtual consultations, digital communications, and data storage.
PHI includes any individually identifiable health information related to:
HIPAA rules apply to "covered entities" including healthcare providers, health plans, and healthcare clearinghouses—essentially anyone providing clinical services through telehealth.
Additionally, "business associates" such as telehealth platform vendors, cloud storage providers, and any third parties handling PHI must also comply with these regulations.
The basic requirements for a HIPAA compliant telehealth platform include:
According to a 2021 survey by the American Medical Association, 85% of physicians reported using telehealth services, highlighting the growing importance of HIPAA compliance in digital healthcare delivery (Source: AMA, 2021).
A HIPAA-compliant telehealth platform provides the technical infrastructure and security measures necessary for healthcare providers to conduct virtual consultations while maintaining patient privacy and data security according to federal regulations.
In essence, these platforms serve as secure digital environments where healthcare providers can interact with patients, share medical information, conduct assessments, and maintain records—all while implementing the safeguards required by HIPAA regulations.
Key characteristics that define a true HIPAA-compliant telehealth platform include the following:
The fundamental difference between standard videoconferencing tools and HIPAA-compliant telehealth platforms is that the latter includes specific security measures, documentation, and practices designed to protect PHI.
While consumer-grade communication tools might offer some security features, they typically lack the comprehensive protections and legal agreements (such as Business Associate Agreements) required for healthcare applications.
Understanding the specific regulations that govern telehealth operations helps providers select appropriate platforms and implement correct procedures.
The following sections detail the four main rules that comprise HIPAA compliance for telehealth services.

The HIPAA Privacy Rule establishes national standards to protect individuals' medical records and personal health information (PHI). It limits how healthcare organizations use, access, and disclose PHI, ensuring patient privacy and promoting trust in healthcare systems.
Key Requirements:
Healthcare organizations must implement clear policies governing who can access patient information and under what circumstances.
For example, front desk staff typically need access to scheduling and billing information but not complete medical histories, while clinical staff require more comprehensive access.
The Privacy Rule also requires organizations to explain clearly how patient information may be used and disclosed, typically through a Notice of Privacy Practices that patients receive during their first encounter.
While the Privacy Rule covers all PHI, the Security Rule focuses explicitly on electronic protected health information (ePHI). This rule requires appropriate administrative, physical, and technical safeguards to ensure confidentiality, integrity, and security. Of electronic health information
The following safeguard measures are crucial under HIPAA.
According to IBM’s 2024 Cost of a Data Breach Report, phishing accounted for 15% of all data breaches and was the second-most costly attack vector, averaging around $4.88 million per breach. (Source: IBM)
In addition, IBM and other cybersecurity sources in 2025 emphasize that AI-generated phishing attacks are becoming more sophisticated.
These emerging threats target executives with hyper-personalized tactics and often bypass standard email filters, further increasing breach costs, which reached an average of approximately $4.9 million in 2024
The Breach Notification Rule requires covered entities and their business associates to provide notification following a breach of unsecured PHI. This rule ensures transparency and allows affected individuals to take protective measures.
Notification Requirements
The rule defines a breach as an impermissible use or disclosure that compromises the security or privacy of PHI. By the end of 2024, hacking and IT incidents were responsible for 276.8 million breached healthcare records, a 64 % increase from 2023, with 14 separate breaches exposing over 1 million records each. (Source: HIPAA Journal)
In March–April 2025, the Yale New Haven Health System experienced a significant breach that exposed the PHI of 5.5 million individuals, highlighting that large-scale incidents are still occurring this year. (Source: HIPAA Journal)
The Enforcement Rule establishes procedures for investigating violations and determining penalties for entities that fail to comply with HIPAA rules. It provides the framework for accountability in the healthcare data protection ecosystem.
The Enforcement Process is as follows.
As of June 2025, the U.S. Department of Health and Human Services (HHS), through its Office for Civil Rights (OCR), has settled or imposed civil money penalties in 152 cases, totaling $144,878,972. (Source: HHS OCR Enforcement Highlights)
In 2024, OCR imposed a $1.5 million civil money penalty against Warby Parker for HIPAA Security Rule violations following a breach involving unauthorized access to customer accounts. (Source: HHS Press Room)
Additionally, OCR initiated its 2024–2025 HIPAA Audits, reviewing 50 covered entities’ and business associates’ compliance with selected provisions of the HIPAA Security Rule, focusing on hacking and ransomware attacks. (Source: HHS HIPAA Audit Program)
Specific technical features are essential to ensure both regulatory compliance and practical security when evaluating or building a HIPAA-compliant telehealth platform.
These features work together to create a comprehensive protection framework for patient data.
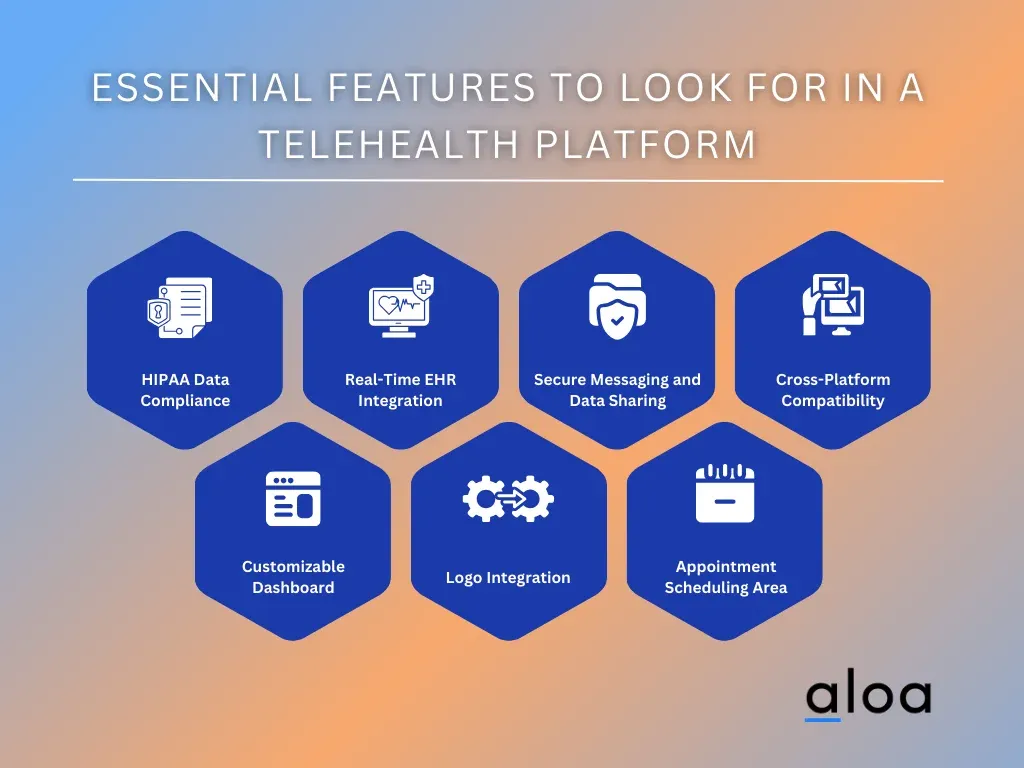
End-to-end encryption ensures that data transmitted between patients and providers remains unreadable even if intercepted.
Healthcare organizations implementing this technology reduce their breach risk by up to 70% (Ponemon Institute, 2023)
Unlike consumer platforms, healthcare-grade video tools provide multi-layer encryption, verify participants’ identities, offer secure waiting rooms, enable session locks, and restrict screen sharing to authorized users for enhanced security.
Role-Based Access Control (RBAC) restricts system access by assigning permissions according to user roles, ensuring staff members can only view or modify information essential to their duties.
A comprehensive RBAC system includes these key features.
Audit logs track who accessed what, when, and what actions were taken—critical for HIPAA compliance and incident investigations.
NIST recommends capturing user ID, event type, timestamp, outcome, and affected data
These secure communication systems replace risky, non-compliant tools like email, SMS, and unregulated messaging apps by offering robust features such as end-to-end encryption, message delivery confirmation, automatic session timeouts, and the ability to wipe sensitive data from compromised devices remotely.
Facilitates, enforces, and manages the legally required Business Associate Agreements (BAAs) between healthcare providers and their vendors, ensuring all parties comply with HIPAA regulations and securely handle protected health information (PHI) throughout their partnership.
Even with the best intentions, healthcare organizations often make critical errors that can compromise HIPAA compliance when implementing telehealth solutions. Being aware of these pitfalls helps in avoiding costly violations.
Using consumer-grade communication tools is a major telehealth compliance failure due to inadequate security features and a lack of Business Associate Agreements (BAAs).
Additionally, improper screen sharing can unintentionally expose PHI, as providers may show other patient records or be in visible locations. Establishing screen-sharing protocols and managing backgrounds can prevent such exposures.
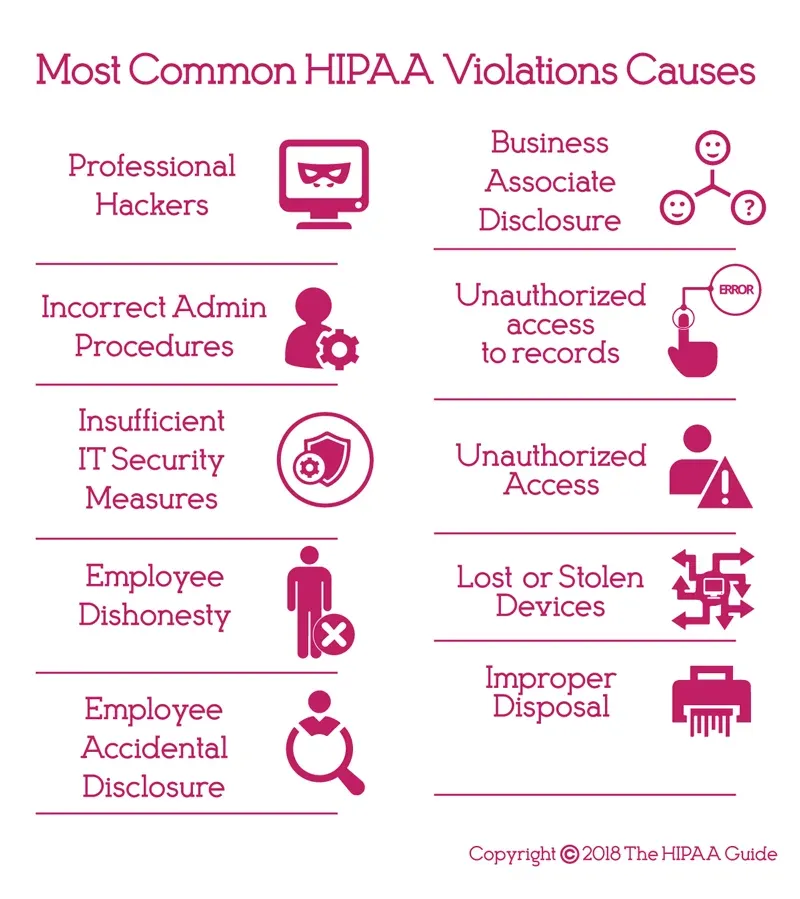
Here are key areas where providers often fall short when deploying a HIPAA compliant telehealth platform:
Missing or inadequate Business Associate Agreements (BAAs) with technology vendors create significant liability.
Any third party that may access, process, or store PHI—including telehealth platform providers, cloud storage services, or technical support teams—must have a properly executed BAA before accessing systems containing patient information. (Source: HIPAA Journal)
While off-the-shelf telehealth platforms may offer convenience, many healthcare organizations find that custom HIPAA compliant telehealth platforms better address their specific needs, workflows, and compliance requirements.
Custom healthcare solutions can be built with an organization's exact security requirements in mind from the beginning, rather than trying to adapt generic platforms to healthcare's stringent requirements.
This approach ensures that all aspects of the platform are tailored to meet specific compliance and operational needs. (Source: Healthcare IT News)
The integration capabilities of custom platforms also represent a significant advantage.
Healthcare providers using telehealth solutions integrated with their existing Electronic Health Record (EHR) systems can experience fewer workflow disruptions and higher provider satisfaction compared to those using standalone telehealth platforms. (Source: Journal of Medical Internet Research)
Custom platforms can accommodate specialty-specific requirements that generic solutions might not address. For example:
From a compliance perspective, custom solutions can be designed with built-in documentation and reporting features specific to an organization's audit procedures and regulatory requirements.
This reduces the administrative burden of compliance and decreases the risk of violations. (Source: Healthcare IT News)
A healthcare system that implements a custom HIPAA compliant telehealth platform tailored to its workflows can achieve ROI through:
A HIPAA-compliant telehealth platform is essential for safe, trusted virtual care. In today’s environment, where data breaches cost millions and damage patient trust, strict adherence to HIPAA protects sensitive data and your organization’s reputation.
HIPAA compliance is more than a checklist; it creates a secure, professional, and efficient digital care environment. This requires a deep understanding of regulations, avoiding common pitfalls, and partnering with technology providers who embed compliance into their solutions from the ground up.
Whether upgrading existing systems or launching new virtual care services, choosing a HIPAA-ready telehealth platform delivers peace of mind and a competitive advantage.
Need help building a customized, secure telehealth platform?
Let’s discuss how AppsRhino’s expertise in healthcare app development can empower your organization.
At AppsRhino, we develop secure, scalable, and fully tailored healthcare management applications that comply with HIPAA standards, allowing you to prioritize patient care while we handle compliance and technology.
Why Choose AppsRhino for Your HIPAA-Compliant Telehealth Platform?
Custom Development
7 Apr 2026
Tell us what your business actually runs on today, and we will map what it takes to make it one system.