
Custom Development
Alcohol Delivery Market Share and Trends: Size, Growth, & Business Opportunities
7 Apr 2026
Anyone at your clinic can legally talk about your health—if you let them.
Most people don’t know that.
From front-desk staff to third-party vendors, your medical details could be seen, shared, or even leaked without your clear say.
That’s where HIPAA steps in.
HIPAA isn't just hospital red tape. It’s a federal law made to protect your health information—what it is, who can see it, and how it's shared.
This guide breaks down the HIPAA rules that patients need to know. In plain language. No fluff. Just the facts that keep your medical data safe.
HIPAA sounds complicated, but it’s not. This federal law exists to protect one thing—your medical privacy.
And yes, it matters every time you go for a check-up, fill a prescription, or even use a fitness app connected to your health record.
Let’s break it down without the jargon.
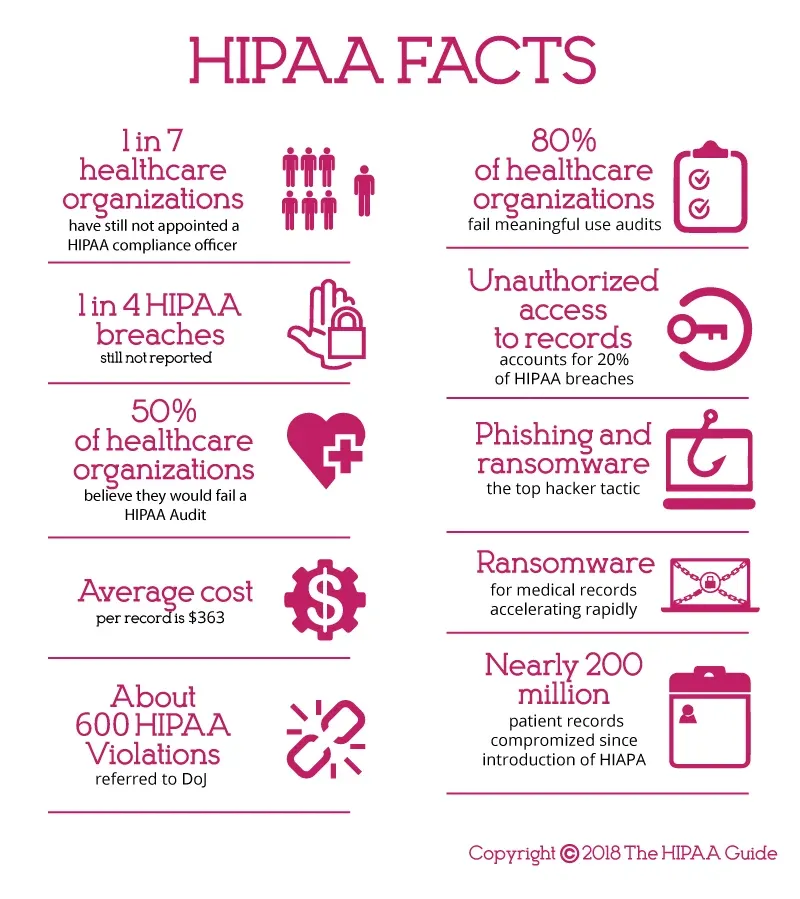
Before HIPAA, your medical info could be passed around easily. Think of it like this: A receptionist could mention your condition out loud, or a clinic could leave your file on the front desk.
The HIPAA rules for patients were made to stop that. They were designed to make sure no one can access or share your health info without your permission.
HIPAA became law in 1996, aiming to fix how health data was handled—especially as healthcare moved to digital.
It’s not just your doctor. HIPAA rules apply to anyone who handles your health info.
That includes:
So, if your hospital uses a third-party healthcare system to process your bills, that vendor must also follow the same rules as your doctor.
Here’s what makes HIPAA work:
Let’s say you visit a pharmacy.
You hand over your insurance card and get a prescription filled. Behind the scenes, your data moves through multiple systems. HIPAA makes sure each one is secure.
That’s the real impact of the HIPAA rules for patients—peace of mind, privacy, and control over who sees your health story.
You don’t need to be a lawyer to understand your health privacy rights. But you do need to know the basics.
The HIPAA rules for patients are designed to protect your data, give you control, and ensure your healthcare experience is safer and more transparent.
Here’s what that looks like in real life.
You can ask to see your medical records. Full stop.
Let’s say you visit three different clinics in a year. You can request your full medical history from each of them—no long forms, no fees (except maybe a small copy fee). They must respond within 30 days.
That includes lab results, scans, prescriptions, and even doctor’s notes.
Example: You had a test done six months ago, and the clinic never followed up. You can ask for that record and review the results yourself.
Medical records aren’t perfect. Typos happen. Incorrect entries do too.
If your file says you have diabetes but you don’t, you can ask for a correction. This matters for future care, insurance, or even travel documentation.
It’s not about rewriting history—it’s about accuracy. And your provider has to respond to your request, even if they don’t agree to change it.
Imagine you find out your health insurer accessed a file without telling you. Under HIPAA rules for patients, you can ask for a list of who’s viewed your records in the past six years.
It doesn’t include every nurse or doctor, but it does include non-routine access—like admin staff or third-party vendors.
This builds trust and makes systems more accountable.
You don’t have to share everything with everyone.
If you tell your doctor, “Please don’t tell my employer I had this test,” they have to honor that—especially if you pay out of pocket. That’s a real HIPAA rule, and it protects your personal decisions.
Patients in sensitive situations—like mental health treatment or testing for STIs—rely on this.
You can ask your provider to send info via email, phone, or mail—whichever feels safe.
Example: If you don’t want lab results mailed to your family home, you can give an alternative address. Or request encrypted email instead of voicemail.
This is about comfort and safety. And it’s one of the most overlooked HIPAA rules for patients
Not every detail stays behind closed doors. But there are strict limits.
Understanding when and why your info gets shared makes it easier to protect your privacy—and ask the right questions.
Your doctor doesn’t need permission to share info with another specialist treating you. Same goes for billing, running lab tests, or insurance claims.
These are called “healthcare operations.” And they’re routine under HIPAA rules.
Example: You break your arm. The ER team can send your records to an orthopedic surgeon for a follow-up—no form-filling needed.
It’s about speed and care continuity
But not everything can be shared freely.
Your consent is required for things like:
Scenario: A hospital wants to feature you in a health campaign. They must ask you first.
This protects you from unexpected exposure—especially in today’s data-driven world.
Doctors can share limited info with people involved in your care—if it’s in your best interest.
Example: You're unconscious in the ER. The nurse can tell your spouse what happened and what treatment you're receiving.
But once you’re awake, you get to decide who’s in the loop
This rule is simple: only share what’s needed.
If a billing clerk needs to confirm your visit date, they shouldn’t see your full diagnosis. Systems must limit access to the bare minimum.
That’s what keeps your info from being overshared.
And that’s what HIPAA rules for patients are built to do—keep your data close, controlled, and respected.
You have the right to see your own health records. But most people don’t know how to ask—or what to do if they’re denied.
Under the HIPAA rules for patients, you can request your records, check for errors, or even send them to someone else. This isn’t just helpful—it’s your legal right.
Let’s break it down
Start by contacting your doctor or hospital. You can ask through a secure patient portal, by email, or by filling out a request form. Most clinics have a form ready to go. Some even let you submit it online.
If you're unsure, call the clinic and ask: “What’s your process for requesting medical records?”
Here's an example:
Maria recently switched doctors and needed her test results from last year. She logged into her clinic’s portal, filled out a simple online form, and got her PDF files within days. Easy. No back-and-forth emails.
You have choices.
You can ask for paper copies, digital files like PDFs, or even have them sent directly to another provider. If you want to use a health app that follows HIPAA rules, they should be able to connect your data directly.
Always state the format you want when you make the request.
They can’t say no just because.
Under the HIPAA rules, they must give a valid reason. If you're denied access, they have to explain why in writing.
If you still disagree, you can file a complaint with the U.S. Department of Health and Human Services (HHS). It’s free and doesn’t require a lawyer
Providers usually have 30 days to respond.
If they need more time, they can ask for a 30-day extension, but they have to tell you why.
They can charge a small fee—but only to cover the cost of copies or digital delivery.
You can’t be charged for asking. Also, they can’t make you come in person just to pick it up.
Under HIPAA rules for patients, access must be simple, affordable, and timely.
Medical records are valuable—not just to you, but to hackers too.
Many data breaches start with one weak link: an open email, a lost phone, or a bad password.
You don’t need to be a tech expert to stay safe.
Just a few small steps can go a long way.
Always use a secure patient portal to view or send records.
These are built to follow HIPAA rules and keep your data safe. Avoid logging in on shared computers or public Wi-Fi.
If you use a mobile app, enable two-factor authentication.
Never share sensitive info by regular email or text. If your clinic wants to send your results that way, ask them to use encrypted platforms instead.
Example: John received his test results over a personal email. Days later, his account was hacked. A simple switch to the clinic's secure portal could’ve prevented it.
This might feel awkward, but it’s important.
Ask: “Do you use cloud-based storage?” or “Is patient data encrypted?”
These small questions can help you understand how seriously they take your privacy.
Posting health updates on social media might seem harmless—but details can be used against you. It’s easy to connect the dots from your posts, especially if your profile is public.
These small questions empower you.
Because at the end of the day, HIPAA rules for patients exist to give you control.
And when used right, that control feels less like a burden—and more like peace of mind.
A health data breach can feel personal. It’s not just numbers or files—it’s your medical history, insurance details, and personal identity.
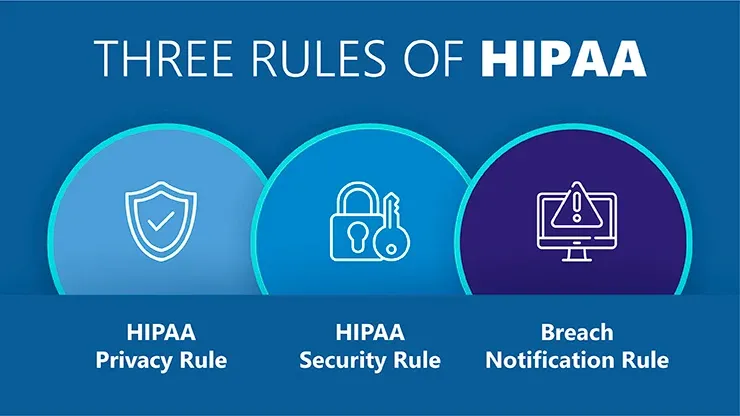
Understanding HIPAA rules for patients can help you know what to expect and how to react when your data is exposed.
A data breach happens when unauthorized people access your protected health information (PHI). Think of it like someone breaking into your digital health file.
For example, a hospital’s system might get hacked, exposing patient records—including yours.
These breaches don’t always come from outside attacks. A misplaced laptop or an employee sharing records without permission can trigger one.
Either way, your private health info could land in the wrong hands.
Under HIPAA rules, healthcare providers must tell you about a breach within 60 days. You’ll likely get a letter explaining what happened and what info was exposed.
Let’s say a clinic’s server was attacked. If your name, birthdate, and treatment details were accessed, you should get a direct notice. It won’t be hidden in fine print.
The notice must include:
This isn’t optional. It’s part of the HIPAA rules for patients to stay informed.
If your info is part of a breach:
Don’t wait for something to go wrong. Stay one step ahead.
When your health information isn’t handled right, you have the right to speak up. Knowing how to file a HIPAA complaint is a key part of using your power under HIPAA rules for patients.
It’s a simple process, and you don’t need legal help to do it.
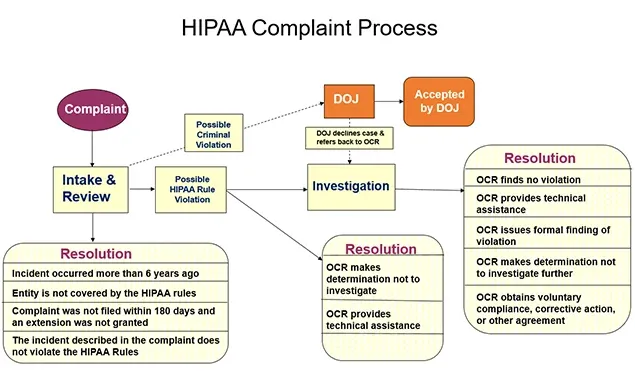
Let’s say a nurse talks about your diagnosis loudly in a hallway. Or a clinic sends your test results to the wrong person. These are clear signs your privacy might have been violated.
Other red flags:
You can file a complaint with the U.S. Department of Health and Human Services (HHS). Do it:
HHS will review your complaint. If it violates HIPAA rules, they may investigate. You’ll get updates, and if needed, action may be taken against the provider.
It’s not just about one case—it helps improve systems for everyone.
If you're planning to build a healthcare app, knowing the basics of HIPAA isn't just helpful—it's a must.
HIPAA gives patients rights like:
Accessing their medical records
Requesting corrections
Controlling who can see their data
Your app must support these actions securely and clearly.
If your app collects or stores any patient info (names, medical history, insurance, etc.), you are expected to:
Keep it private
Use secure systems
Follow HIPAA’s privacy and security rules
Failure to do so can lead to legal trouble or loss of user trust.
Patients and providers want tools they can rely on. A HIPAA-compliant app:
Shows you take privacy seriously
Meets industry standards
Reduces risk of data breaches or complaints
Before development starts:
Understand the rules
Map out key HIPAA requirements
Work with developers who know healthcare compliance
This helps you avoid costly fixes later and ensures a smoother approval process.
Understanding HIPAA rules for patients puts you in the driver’s seat. It's not just about rules — it’s about your right to control your health data.
Whether you're visiting a specialist or using a mobile health app, knowing your privacy rights can protect your information from misuse.
You have the right to access your medical records, request corrections, and know who’s viewed your data.
For instance, if a hospital shares your test results without permission, you have the power to take action.
That’s where HIPAA rules for patients step in — they back you up legally.
Imagine you switch doctors and your records go missing. Or your insurance denies a claim based on outdated info. Knowing the HIPAA rules means you can spot red flags early and fix them. That’s real ROI — less stress, fewer errors, and more control.
Custom Development
7 Apr 2026
Tell us what your business actually runs on today, and we will map what it takes to make it one system.