
Custom Development
Alcohol Delivery Market Share and Trends: Size, Growth, & Business Opportunities
7 Apr 2026
The Health Insurance Portability and Accountability Act (HIPAA) establishes critical standards that safeguard sensitive patient data from unauthorized access and disclosure, ensuring the privacy and security of those we serve.
This comprehensive guide breaks down the four main HIPAA rules in plain language, showing exactly who must comply, what each rule requires, and how to implement practical safeguards effectively within your organization.
We explore who needs to be HIPAA compliant, examine common compliance mistakes that many organizations make, and provide actionable steps for maintaining compliance to help you avoid penalties and protect your practice.
Whether you're a clinic administrator, healthcare IT professional, or technology vendor handling patient data, you'll find clear and concise guidance to navigate the complexities of healthcare compliance with confidence, empowering you to protect both your patients & your organization.
The Health Insurance Portability and Accountability Act (HIPAA) provides critical rules protecting your health information while allowing the essential data flow necessary for delivering quality healthcare.
These regulations establish comprehensive standards for maintaining the confidentiality, integrity, and accessibility of patient data.
Specifically, HIPAA outlines the procedures healthcare organizations must follow to manage both paper and electronic health records (EHRs) to safeguard sensitive information.
The information HIPAA protects is called Protected Health Information (PHI). This includes various data types such as your medical history, insurance details, billing information, and laboratory test results.
As healthcare systems increasingly transition to digital formats, the significance of HIPAA in protecting patient privacy and data security has grown manifold.
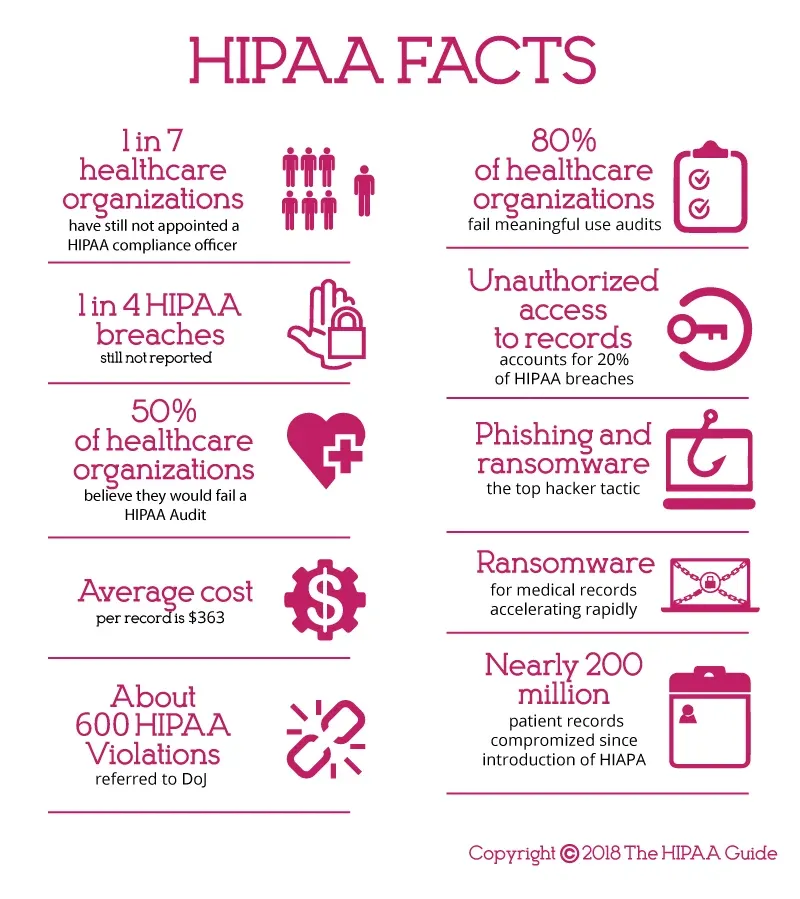
With more patient data stored electronically and in the cloud, understanding and adhering to HIPAA rules is crucial for managing associated risks. These standards apply to health plans, healthcare clearinghouses, and providers involved in specific healthcare services. (Source: HHS.gov)
Understanding who must follow HIPAA rules is essential for proper compliance. The regulations cast a wide net across the healthcare industry, affecting organizations even when they might not realize their obligations.
These organizations are subject to HIPAA rules: healthcare providers like hospitals, clinics, pharmacies, and nursing homes; health plans including insurers and Medicare; and healthcare clearinghouses that process health information into standard formats for secure, compliant use.
Any person or organization handling PHI for a covered entity must follow HIPAA rules. This includes billing services, IT vendors, cloud providers, consultants, and software developers who manage or access protected health information on the entity’s behalf.
Entities that perform functions or activities on behalf of, or provide certain services to, a covered entity that involve the use or disclosure of protected health information (PHI).
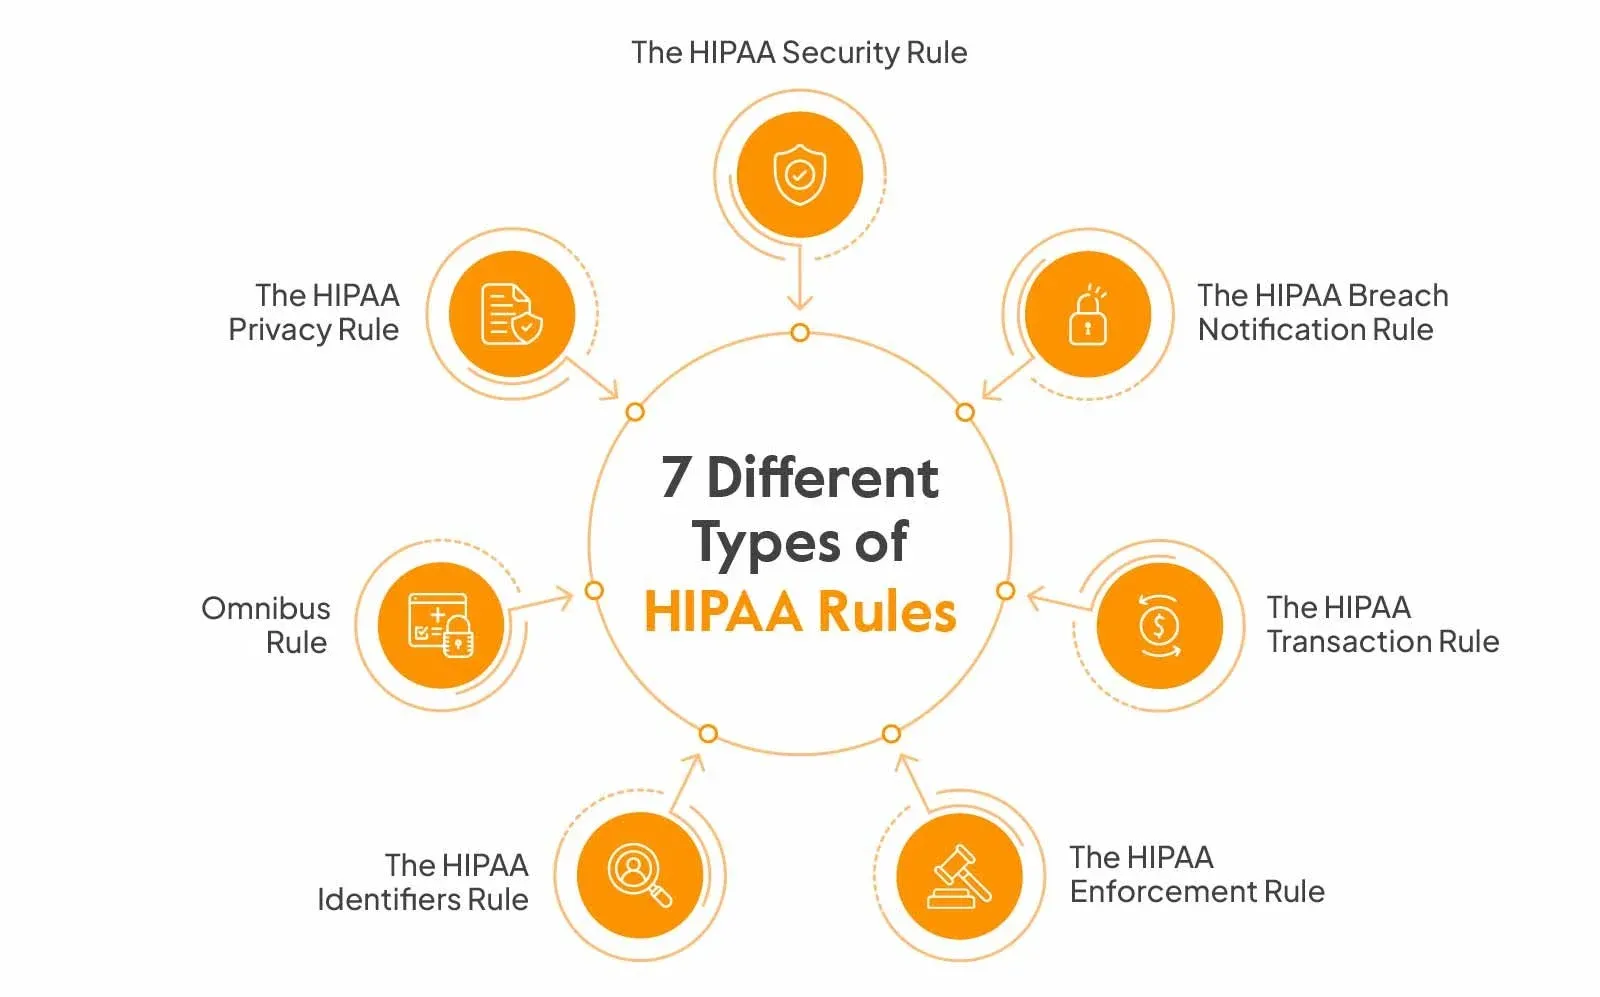
HIPAA regulations are divided into four primary rules, each addressing different aspects of protecting patient information. Understanding these components is crucial for implementing effective compliance programs.
The HIPAA Privacy Rule establishes national standards to protect individuals' medical records and personal health information (PHI). It limits how healthcare organizations use, access, and disclose PHI, ensuring patient privacy and promoting trust in healthcare systems.
Key Requirements
Healthcare organizations must implement clear policies governing who can access patient information and under what circumstances.
For example, front desk staff typically need access to scheduling and billing information but not complete medical histories, while clinical staff require more comprehensive access.
The Privacy Rule also requires organizations to explain clearly how patient information may be used and disclosed, typically through a Notice of Privacy Practices that patients receive during their first encounter.
While the Privacy Rule covers all PHI, the Security Rule focuses explicitly on electronic protected health information (ePHI).
This rule requires appropriate administrative, physical, and technical safeguards to ensure confidentiality, integrity, and security. Of electronic health information.
The following safeguard measures are crucial under HIPAA.
According to IBM’s 2024 Cost of a Data Breach Report, phishing accounted for 15% of all data breaches and was the second-most costly attack vector, averaging around $4.88 million per breach. (Source: IBM)
In addition, IBM and other cybersecurity sources in 2025 emphasize that AI-generated phishing attacks are becoming more sophisticated.
These emerging threats target executives with hyper-personalized tactics and often bypass standard email filters, further increasing breach costs, which reached an average of approximately $4.9 million in 2024
The Breach Notification Rule requires covered entities and their business associates to provide notification following a breach of unsecured PHI.
This rule ensures transparency and allows affected individuals to take protective measures.
Notification Requirements
The rule defines a breach as an impermissible use or disclosure that compromises the security or privacy of PHI. By the end of 2024, hacking and IT incidents were responsible for a record 276.8 million breached healthcare records, a 64 % increase from 2023, with 14 separate breaches exposing over 1 million records each. (Source: HIPAA Journal)
In March–April 2025, the Yale New Haven Health System experienced a significant breach that exposed the PHI of 5.5 million individuals, highlighting that large-scale incidents are still occurring this year. (Source: HIPAA Journal)
The Enforcement Rule establishes procedures for investigating violations and determining penalties for entities that fail to comply with HIPAA rules. It provides the framework for accountability in the healthcare data protection ecosystem.
The Enforcement Process is as follows.
As of June 2025, the U.S. Department of Health and Human Services (HHS), through its Office for Civil Rights (OCR), has settled or imposed civil money penalties in 152 cases, totaling $144,878,972. (Source: HHS OCR Enforcement Highlights)
In 2024, OCR imposed a $1.5 million civil money penalty against Warby Parker for HIPAA Security Rule violations following a breach involving unauthorized access to customer accounts. (Source: HHS Press Room)
Additionally, OCR initiated its 2024–2025 HIPAA Audits, reviewing the compliance of 50 covered entities and business associates with selected provisions of the HIPAA Security Rule, with a focus on hacking and ransomware attacks. (Source: HHS HIPAA Audit Program)
Achieving HIPAA compliance is an ongoing, organization-wide effort involving administrative, physical, and technical safeguards.
It requires the implementation of procedures and continuous monitoring and updating to ensure patient data is secure and that legal obligations are met. The HIPAA rules provide the regulatory foundation for all these efforts.
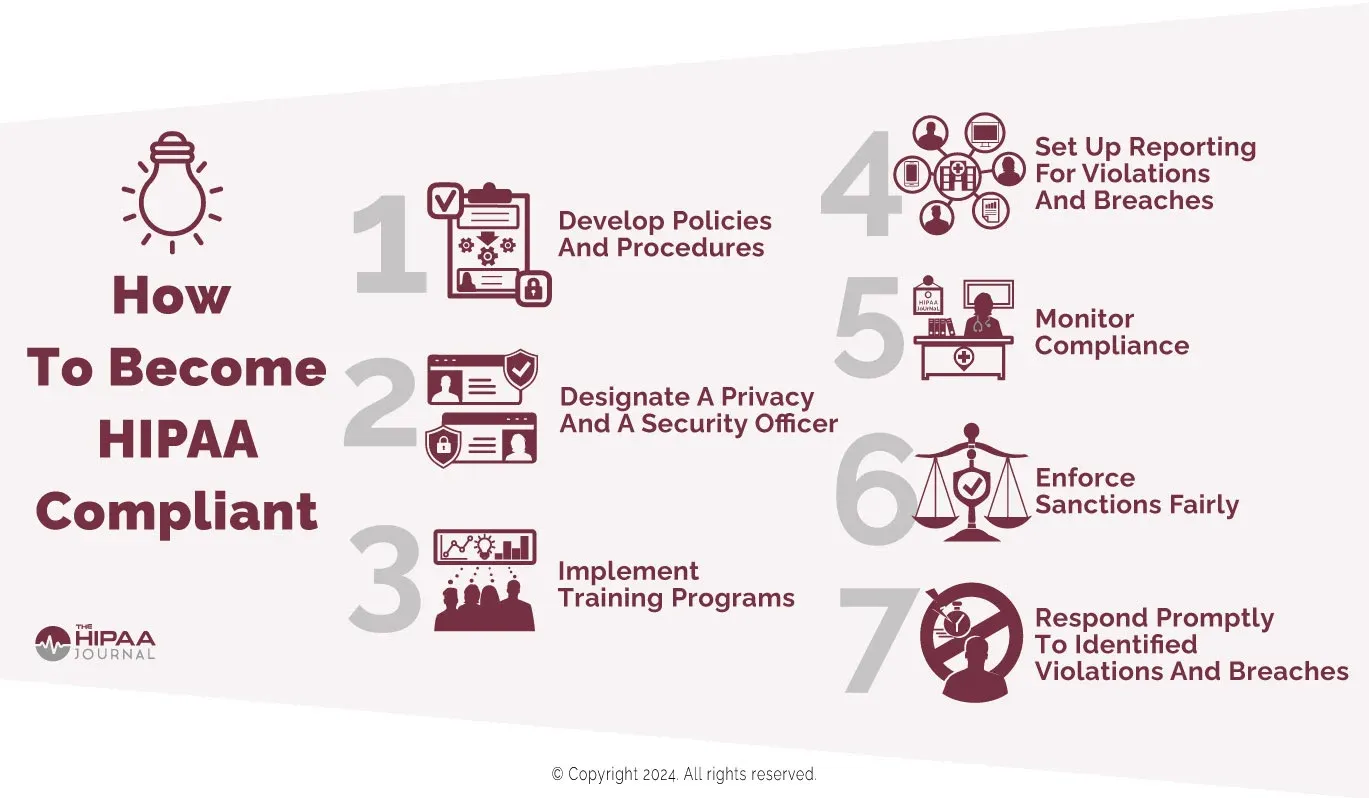
Under the HIPAA Security Rule, organizations must conduct a thorough and accurate assessment of potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic Protected Health Information (ePHI).
This includes identifying internal and external threats, evaluating the likelihood and impact of those threats, and implementing security measures to reduce risks to a reasonable and appropriate level.
This is one of the most frequently cited deficiencies in OCR enforcement actions, demonstrating how critical this step is to satisfying HIPAA rules.
Organizations must develop and maintain written policies and procedures that address all aspects of HIPAA compliance, including the HIPAA Privacy Rule, Security Rule, and Breach Notification Rule.
These policies should be tailored to the organization’s operations and regularly updated to reflect regulatory changes or new technologies.
Failing to document and enforce these policies can result in significant violations of HIPAA rules.
All workforce members, including part-time and temporary employees, must receive HIPAA training.
According to HIPAA rules, all workforce members must undergo training at least annually, as well as whenever there are significant changes in policies, procedures, or regulations related to handling protected health information (PHI).
This training is essential to ensure ongoing compliance with HIPAA requirements and cultivate a culture of accountability, vigilance, and awareness throughout the organization.
The HIPAA Security Rule mandates organizations to implement technical safeguards that protect electronic Protected Health Information (ePHI) from unauthorized access, alteration, or destruction.
These safeguards include encryption, access controls, audit logs, and authentication protocols.
Properly implementing these controls is essential to prevent data breaches and maintain compliance with HIPAA requirements.
HIPAA rules require covered entities to establish formal agreements with business associates who handle Protected Health Information (PHI) on their behalf.
These Business Associate Agreements (BAAs) define each party’s responsibilities for safeguarding PHI and reporting any data breaches.
Effective management of business associates ensures compliance and helps prevent unauthorized disclosures.
HIPAA compliance is an ongoing obligation requiring continuous monitoring, reassessment, and improvement.
Organizations must regularly audit their systems, update risk management strategies, and adapt policies to new threats or regulatory changes.
This proactive approach helps prevent data breaches and maintains alignment with HIPAA standards over time.
In today's healthcare landscape, understanding HIPAA regulations is crucial. This article explores common mistakes organizations make, ensuring compliance and protecting patient privacy.
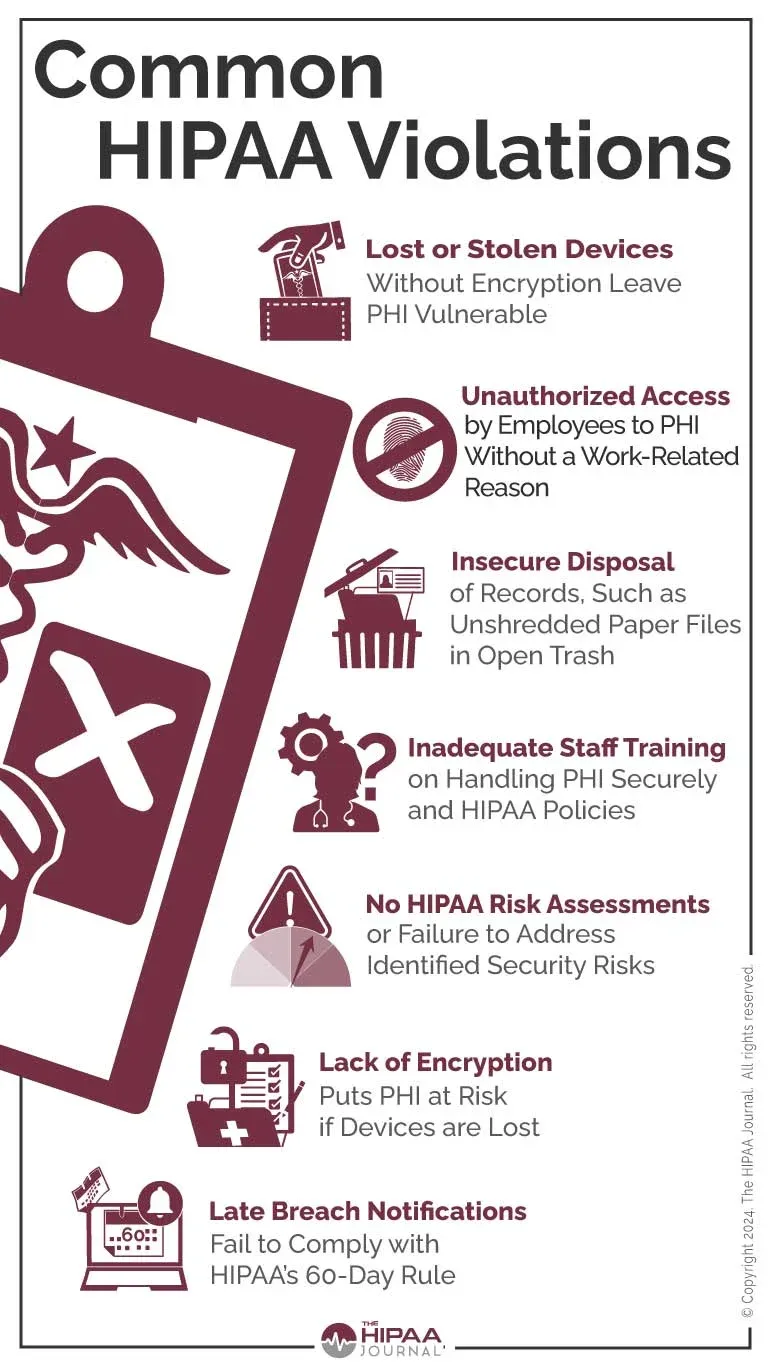
A practical risk analysis is paramount to uncovering potential threats and vulnerabilities within an organization.
Failing to identify all such risks can lead to significant gaps in adherence to HIPAA regulations, potentially resulting in legal penalties, data breaches, and compromised patient confidentiality, thereby jeopardizing the integrity of healthcare delivery.
Business Associate Agreements (BAAs) ensure that external partners comply with HIPAA regulations.
Without compliant BAAs, healthcare organizations can face severe repercussions, including audits and financial penalties. It is critical to actively monitor these associates to ensure they meet the required privacy and security standards for protected health information.
Password security is a foundational aspect of protecting sensitive healthcare information.
The widespread use of shared or weak passwords creates significant vulnerabilities within healthcare environments, increasing the risk of unauthorized access to sensitive patient data.
Establishing strong, unique password policies is essential for safeguarding health information from breaches and other cyber threats.
The HIPAA Security Rule mandates that protected health information (PHI) access is restricted and aligned with specific job responsibilities.
Insufficient access controls can lead to unauthorized access or disclosure of sensitive patient data. Implementing strict role-based access policies is vital to ensure compliance and maintain the confidentiality and security of PHI.
The rise of mobile devices in healthcare has introduced new security risks, particularly when these devices are not adequately secured.
Unsecured mobile devices are a leading cause of PHI breaches, putting patient information at risk.
Organizations must implement robust security measures, such as encryption and device management policies, to protect sensitive health data on mobile platforms.
Proper disposal of protected health information (PHI) is critical to enforcing HIPAA rules.
Discarding physical records improperly, such as tossing them in the trash or failing to wipe electronic devices adequately, can lead to unauthorized access to sensitive information.
Implementing secure disposal methods is essential for maintaining compliance and protecting patient privacy.
The HIPAA rules including the Privacy, Security, Breach Notification, and Enforcement Rules, form a comprehensive legal framework to protect sensitive patient information in a rapidly digitalizing healthcare landscape.
By following the HIPAA rules and focusing on risk assessments, technical safeguards, workforce training, and diligent vendor management, healthcare organizations can protect patients and their reputations.
Partnering with technology experts like AppsRhino can simplify this complex compliance journey. AppsRhino offers tailored software solutions designed to automate risk management, enhance security protocols, and streamline vendor oversight, helping healthcare providers stay HIPAA compliant while focusing on patient care and innovation.
As healthcare evolves with AI, telemedicine, and mobile technologies, compliance with HIPAA rules must also adapt. Organizations prioritizing this responsibility will be better prepared for threats and opportunities ahead.
Custom Development
7 Apr 2026
Tell us what your business actually runs on today, and we will map what it takes to make it one system.