
Custom Development
Alcohol Delivery Market Share and Trends: Size, Growth, & Business Opportunities
7 Apr 2026
Privacy doesn’t always mean safety.
In fact, most healthcare breaches happen because people think they’re already compliant. They assume HIPAA is a checkbox—tick it once, and you're done. That mindset is dangerous. The rules are strict, and the penalties are real. But the truth is, compliance isn’t just about rules. It’s about habits, systems, and constant awareness.
In this guide, we’ll break down what HIPAA actually requires and how you can build a process that keeps you—and your patients—safe. Not just technically compliant, but confidently secure.
Understanding the HIPAA rules in healthcare isn't just about compliance—it's about building patient trust, protecting sensitive data, and avoiding penalties that could cost millions.
These rules lay the foundation for how healthcare providers handle patient data safely and ethically. Let’s break down the three core HIPAA Rules in healthcare you need to know.
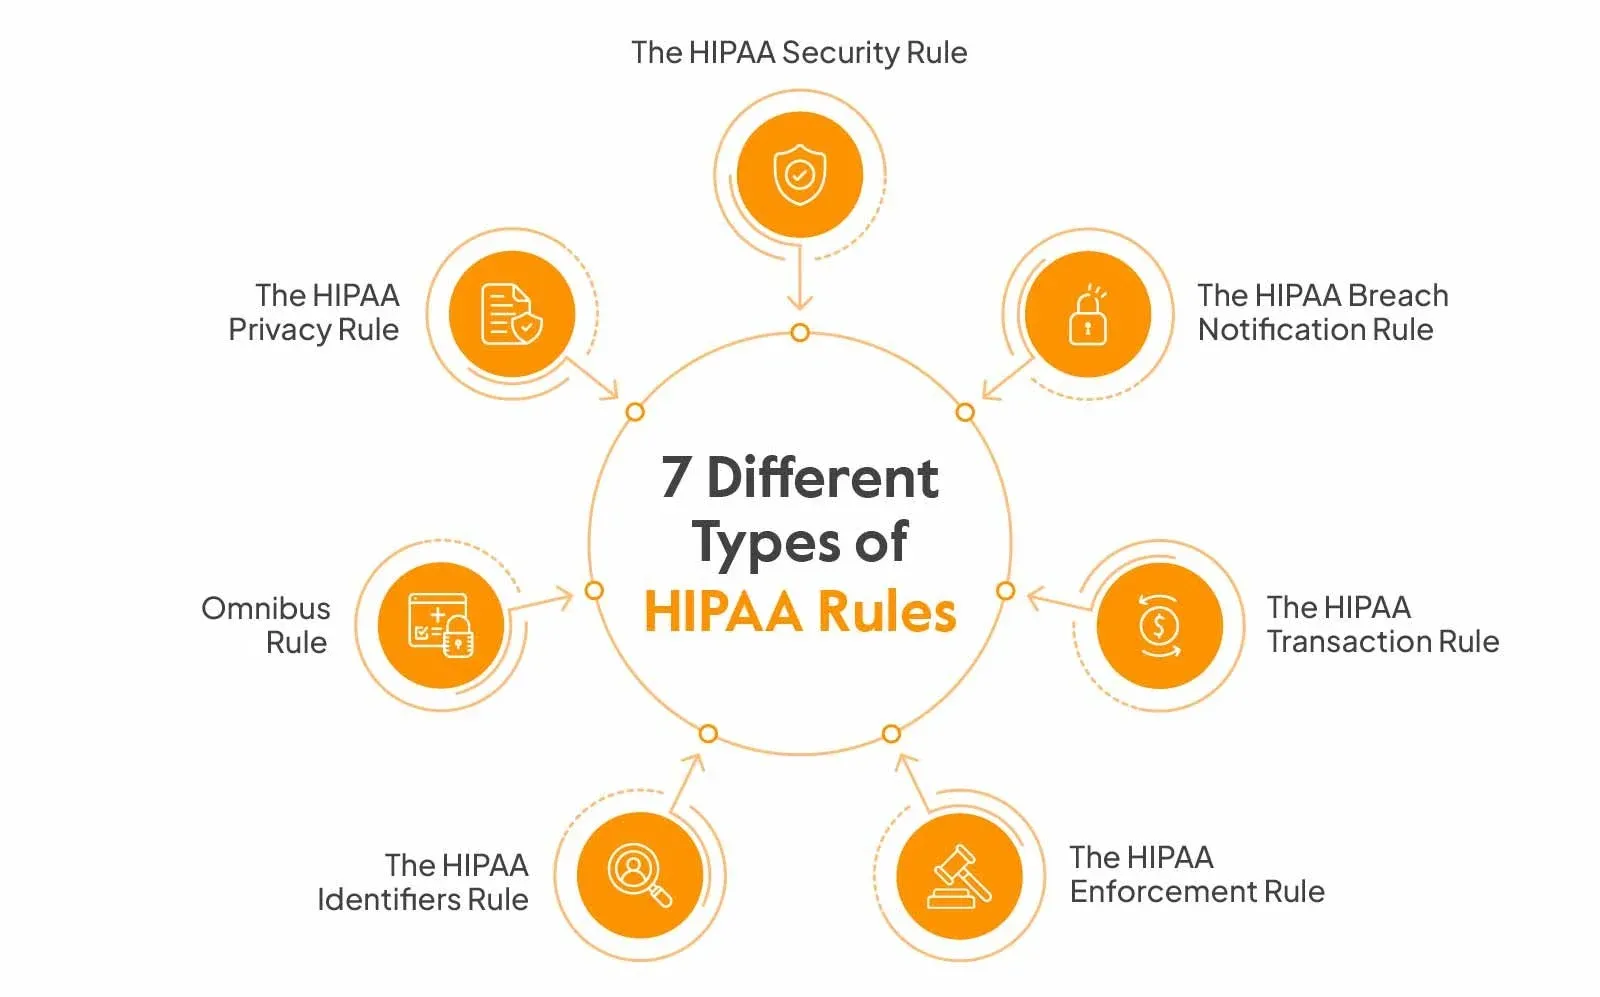
This rule sets clear boundaries on who can access personal health information and under what conditions. It's not just about keeping data private—it’s about putting patients in control of their health information.
For example, if a clinic receptionist shares a patient’s diagnosis with a friend out of curiosity, it’s a violation. The HIPAA rules in healthcare say that only authorized individuals—like the treating doctor or the billing department—should have access, and only when needed.
Patients also have rights under this rule. They can ask to see their records, request corrections, and decide who else can view their information. This empowers patients, builds transparency, and saves time during follow-ups.
By staying aligned with the Privacy Rule, healthcare organizations reduce legal risk while improving patient relationships—a win-win for ROI and trust.
The Security Rule focuses on protecting electronic protected health information (ePHI). It ensures that digital systems used to store and transmit health data are secure.
There are three types of safeguards involved:
Imagine a hospital using outdated systems without two-factor authentication. A hacker could easily breach records. By applying the Security Rule correctly, such attacks can be blocked.
Investing in this security isn’t just about compliance—it reduces downtime, avoids fines, and protects your brand’s reputation. It also aligns with modern trends in healthcare data management and cybersecurity.
This rule requires healthcare providers to notify affected parties if a data breach occurs. But not every incident counts as a breach.
A true breach happens when unsecured PHI is accessed, used, or disclosed in a way not permitted by the HIPAA Rules in healthcare. If a nurse accidentally emails a patient file to the wrong person, that’s a breach.
The timeline matters. Providers must notify patients within 60 days of discovering the breach. If more than 500 people are affected, media outlets and the Department of Health and Human Services must also be informed.
This rule keeps organizations accountable. It forces quick action, which limits damage and builds credibility. Plus, knowing what qualifies as a breach helps teams avoid panic over minor incidents.
In a world where one mistake can go viral, following this rule offers long-term protection—for both patients and providers.
Even with the best intentions, violations of the HIPAA rules in healthcare happen more often than you'd think.
These issues aren't always technical—they’re usually basic oversights that can lead to massive fines and trust loss.
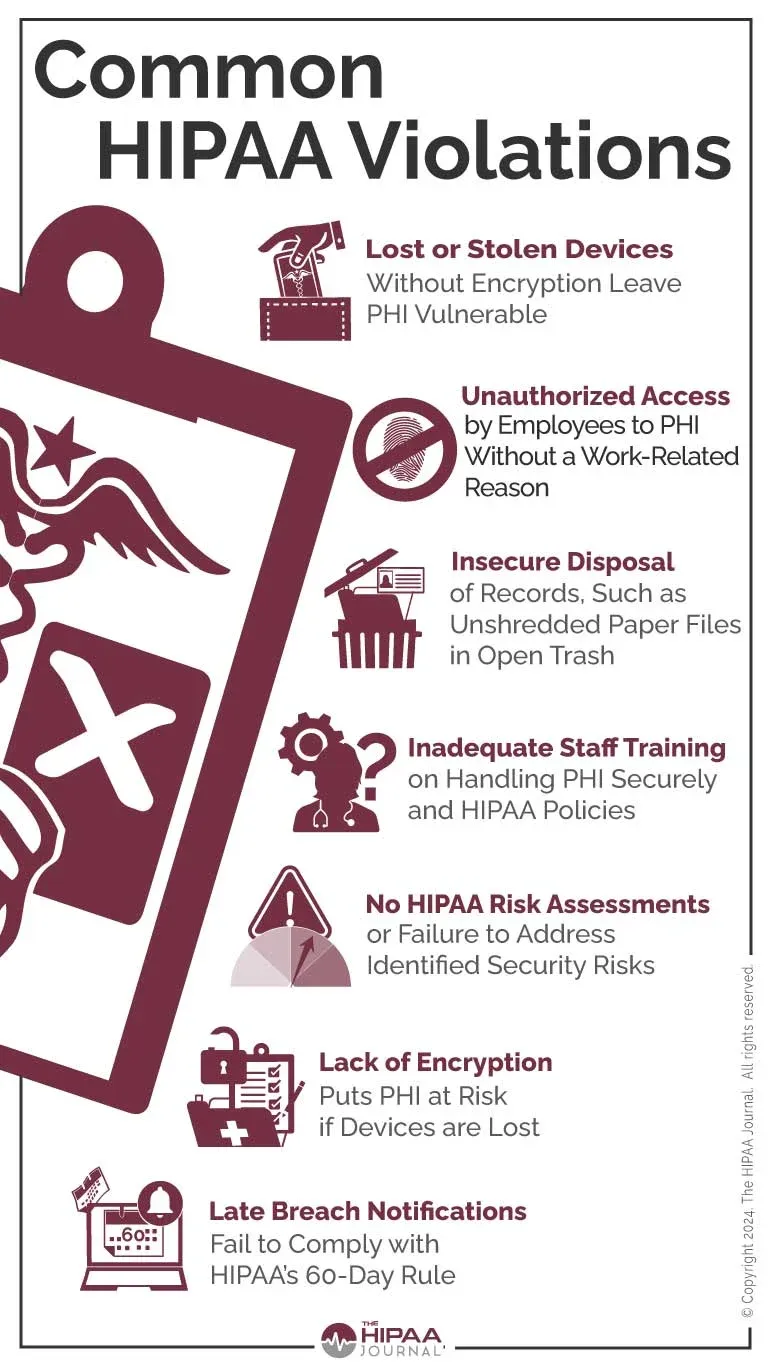
Let’s say a hospital staff member checks out their neighbor’s lab results “just to see.” That’s a clear violation. Access should always be tied to care, billing, or operational needs.
A doctor’s unencrypted laptop gets stolen from a coffee shop. Now thousands of patient records could be exposed.
Portable devices should always be encrypted or remotely wipeable to stay compliant with HIPAA Rules.
Sending patient info over email without proper encryption is still one of the most common mistakes. Encryption isn’t optional—it’s a basic layer of defense.
Dumping paper records into a public trash bin? That’s a serious breach. All records, digital or physical, need secure destruction methods—like shredding or data wiping.
Violations don’t just lead to fines—they harm your brand. Staying compliant is easier when teams are trained, systems are updated, and protocols are followed with zero shortcuts.
It's the foundation of reliable, future-proof healthcare delivery with HIPAA.
Staying compliant with HIPAA rules in healthcare isn’t just about ticking boxes. It’s about building a system where patient trust and safety come first.
Whether you’re running a clinic, a telehealth platform, or a healthcare app, these steps will help make compliance part of your day-to-day operations.
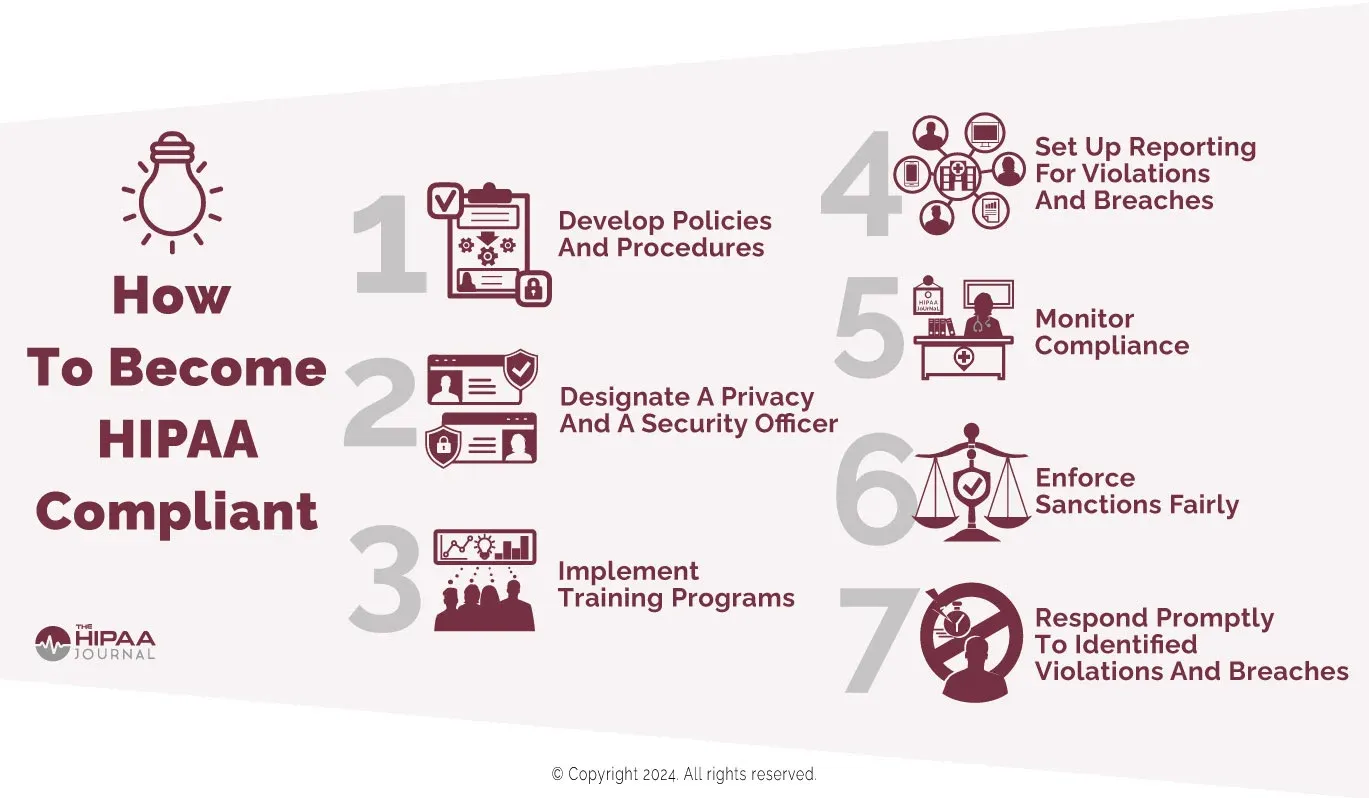
If your staff doesn’t understand the rules, even the best systems can fail. That’s why training isn’t optional — it’s essential. But the training should be regular and easy to follow.
No one wants to sit through hour-long lectures packed with legal jargon.
Let’s say your front desk staff receives a call from someone claiming to be a patient’s relative. Without proper training, they might share sensitive health details — violating HIPAA Rules.
Instead, a trained staff member would know to ask for the proper consent before disclosing anything.
This builds a culture where everyone knows how to protect patient data.
The fewer people who can view or change health data, the lower your risk. This step is about role-based access.
Your marketing intern shouldn’t see patient diagnoses, and your admin team doesn’t need access to clinical notes.
A real-world case: A receptionist accidentally accessed a patient’s mental health file while updating contact info.
That breach could’ve been avoided if their access was limited only to contact fields.
To stay compliant:
This not only protects data but builds internal accountability.
Every bit of patient information — digital or printed — needs protection. Using encrypted systems means even if someone intercepts the data, it’s unreadable.
Think of it as locking each file inside a digital vault.
HIPAA rules in healthcare clearly require strong safeguards. That includes:
Consider this scenario: A clinic stores patient files on a shared Google Drive folder without encryption. One employee uses a weak password.
That’s all it takes for a hacker to access private records.
By switching to a HIPAA-compliant platform with built-in encryption, you instantly reduce that risk.
It’s not just about ticking a rule — it’s about real ROI. Secure systems prevent costly lawsuits and save your brand’s reputation.
Imagine a nurse needs to email a patient their test results. If there’s no clear guideline, they might send it via personal Gmail — a serious violation.
That’s why written policies matter. They tell your staff:
These aren’t just paperwork — they’re guardrails.
You can also make them easier to follow by:
Having these policies in place keeps your entire team aligned and reduces guesswork.
Even with strong systems, breaches can happen. A stolen laptop, a phishing email, or a misdirected file — all it takes is one mistake.
That’s why your breach response plan should be ready before it’s needed.
Here’s what a good plan includes:
Let’s say an email with patient data was accidentally sent to the wrong person. If your team freezes in panic, that delay can cost thousands — or more.
But if there’s a clear plan and regular drills, your team knows exactly what to do. They respond fast, report early, and control the damage.
Regular testing of the plan is key. Once every quarter, simulate a breach. Review what worked and what didn’t. Update the plan based on lessons learned.
Staying ready minimizes the damage — and keeps your practice compliant under pressure.
Think of this as your quick-glance compliance cheat sheet. These items help you follow HIPAA rules in healthcare every single day — without overcomplicating your workflow.
Use this checklist to review your systems, train your staff, and audit your processes.
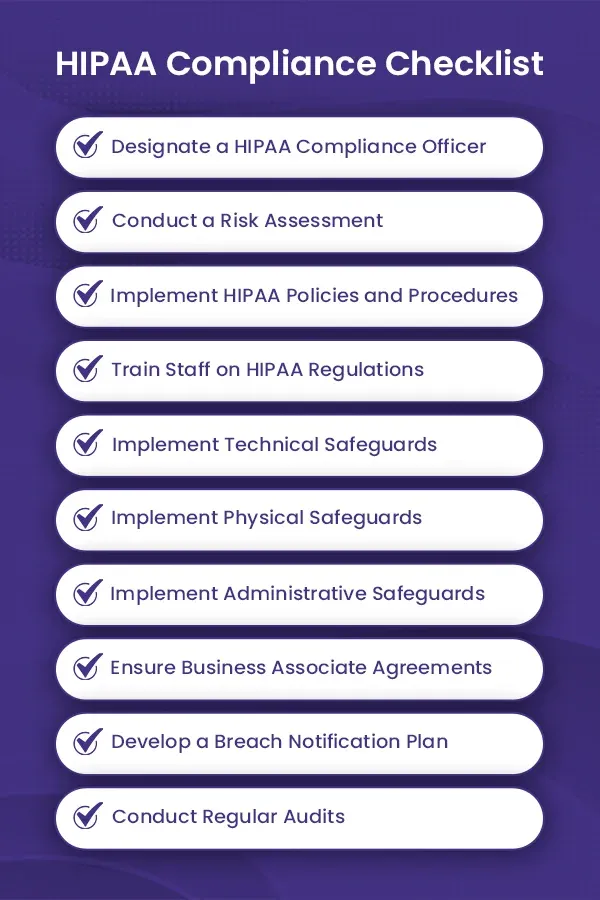
✅ Day-to-Day Compliance Essentials
Let’s say a staff member finds an old USB with patient files from last year. If they’re trained to report it and your checklist is in place, that risk is neutralized fast.
This simple, repeatable list builds confidence. It helps your staff act fast. And it ensures you stay compliant — without guesswork.
When done right, following HIPAA rules in healthcare doesn’t feel like a burden. It becomes a system that protects your patients, improves trust, and safeguards your business.
Staying compliant with HIPAA rules in healthcare isn't about buying the most expensive software. It's about picking tools that protect patient data while keeping daily operations simple and efficient.
The right tech stack allows your team to focus on care—not compliance stress. Below are three essential tool types you should consider.
Start with secure communication. Most HIPAA breaches start with casual, unprotected messages. Email threads, unencrypted apps, or texts—these are risky if you’re discussing patient details.
What these apps do
Real example
A California-based hospital rolled out TigerConnect, a HIPAA-compliant messaging platform. It cut their internal response times by 25%, thanks to real-time chat. No more delays. No more security gaps.
Why it matters
Under HIPAA Rules, you need to track, encrypt, and secure every interaction involving Protected Health Information (PHI). Messaging apps like TigerConnect or Spruce make this effortless.
Bonus benefit
Most platforms integrate with your current EMRs or scheduling tools. That means faster adoption—and better ROI—without disrupting your existing system.
Patient records need more than just a cloud folder. They need encrypted, access-controlled storage that meets compliance standards.
What secure storage does
Real example
A private clinic in Florida switched to Dropbox Business with HIPAA support. They eliminated local servers and cut IT costs by 40%. No more patch updates. No on-site backups. Just secure, scalable file access.
Why it matters
HIPAA rules in healthcare mandate protection of sensitive data, even when stored. Cloud storage platforms like Google Workspace (with BAA) and Dropbox offer pre-built compliance frameworks—no need to build one from scratch.
Ease of use
Your team can upload, tag, and access records just like using a regular cloud folder. No steep learning curve.
You can’t protect what you can’t track. Access logs tell you who viewed or downloaded what—critical for preventing unauthorized use.
What access logging does
Real example
A dermatology clinic in Texas caught a data breach in progress. A former employee tried to download patient lists at 2 AM. Thanks to Azure’s built-in access logging, they were notified immediately—and shut it down.
Why it matters
HIPAA Rules require audit trails. Access logs help you meet that requirement—and give you visibility across your system. AWS, Microsoft Azure, and other platforms offer this feature out of the box.
Pro tip
Set alerts for suspicious behavior. It's proactive security without the manual work.
Navigating HIPAA regulations might feel overwhelming, but compliance is non-negotiable when it comes to safeguarding patient data and building trust. By understanding the core rules—Privacy, Security, and Breach Notification—and implementing the right administrative, technical, and physical safeguards, healthcare organizations can avoid hefty penalties and reputational damage.
But compliance isn’t just about checking boxes. It’s about having the right systems and partners in place to simplify and automate secure data handling.
That’s where AppsRhino comes in.
At AppsRhino, we build custom, HIPAA-compliant healthcare solutions that prioritize both data security and user experience. Whether you're launching a telemedicine app, managing patient records, or developing an all-in-one healthcare platform, our team ensures your product is built to meet all HIPAA standards—right from Day 1.
Ready to build smart, secure, and compliant healthcare apps?
Partner with AppsRhino and move forward with confidence.
Custom Development
7 Apr 2026
Tell us what your business actually runs on today, and we will map what it takes to make it one system.